ToxicPanda 2.0 and GoldDigger: Evolving Android Banking Threats
The emergence of ToxicPanda 2.0 and GoldDigger highlights the growing sophistication of Android banking malware. This article delves into how these threats exploit vulnerabilities and the implications for users and businesses.
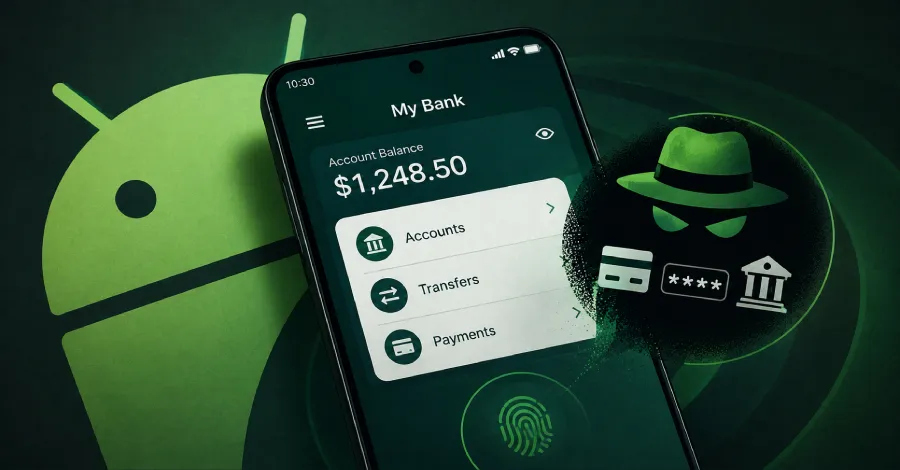
The landscape of cybersecurity threats is constantly evolving, and recent developments in Android banking malware underscore just how sophisticated these attacks have become. Two notable players in this nefarious realm are ToxicPanda 2.0 and GoldDigger, both of which have expanded their capabilities to execute on-device fraud. As mobile banking continues to rise in popularity, the risks associated with these threats pose serious implications for users and businesses alike.
ToxicPanda 2.0 and GoldDigger are not just names; they represent the forefront of a new wave of banking malware that exploits weaknesses in Android devices to siphon off sensitive financial information. The evolution of these malicious tools highlights a significant pivot in the tactics used by cybercriminals, making it imperative for both individuals and businesses to understand the nature of these threats and the steps they can take to mitigate their risks.
Understanding the Threat Landscape
The rise of mobile banking has created a lucrative target for cybercriminals. According to a recent report, mobile banking is expected to reach a market size of $1.82 trillion by 2024, making it an increasingly attractive avenue for fraud. As financial institutions invest heavily in mobile applications to facilitate user transactions, fraudsters leverage advanced malware like ToxicPanda 2.0 and GoldDigger to exploit vulnerabilities in these platforms.
ToxicPanda 2.0, a successor to its earlier version, has introduced improved techniques that allow it to bypass traditional security measures. This variant employs sophisticated obfuscation methods, making it difficult for antivirus software to detect its presence. It not only steals banking credentials but also has the capability to manipulate device functionalities to execute unauthorized transactions.
The Mechanics of ToxicPanda 2.0
ToxicPanda 2.0 operates by embedding itself into legitimate applications, often masquerading as updates or plugins. Once installed, it can:
- Capture keystrokes to record sensitive information.
- Intercept SMS messages for two-factor authentication codes.
- Modify or replace legitimate banking apps with counterfeit versions.
These tactics represent a significant escalation in the sophistication of mobile banking threats, leading to increased instances of financial fraud.
The GoldDigger Malware: A New Contender
GoldDigger has emerged as another key player in the Android banking malware space. Like ToxicPanda 2.0, GoldDigger utilizes on-device fraud techniques to access sensitive financial data. However, it differentiates itself through its use of social engineering tactics to lure users into downloading malicious applications.
GoldDigger typically targets users through fake ads or phishing campaigns that convince them to install seemingly harmless applications. Once active, GoldDigger can:
- Access device permissions to read contacts, messages, and call logs.
- Steal passwords and other credentials stored in browsers.
- Initiate unauthorized transactions by manipulating banking applications.
This malware's ability to manipulate user behavior makes it particularly dangerous, as it can lead to significant financial losses before users even realize they have been compromised.
Real-World Impact of Android Banking Malware
The consequences of these advanced banking threats extend beyond individual users. Businesses, particularly those in the financial sector, may face severe repercussions, including:
- Financial losses from fraud and chargebacks.
- Reputational damage leading to loss of customer trust.
- Legal liabilities stemming from data breaches.
In the wake of these threats, organizations must prioritize cybersecurity measures, including robust authentication protocols, regular security audits, and employee training to recognize and respond to phishing attempts. The financial implications of neglecting these threats can be dire, with estimates suggesting that cybercrime could cost businesses as much as $6 trillion annually by 2021.
Protecting Against On-Device Fraud
Given the sophistication of ToxicPanda 2.0 and GoldDigger, users and businesses must adopt a proactive approach to cybersecurity. Here are several strategies to consider:
- **Utilize Strong Passwords:** Use complex, unique passwords for banking applications and change them regularly.
- **Enable Two-Factor Authentication (2FA):** This adds an extra layer of security, making it more difficult for attackers to gain access.
- **Install Security Software:** Use reputable antivirus and anti-malware solutions to detect and block threats.
- **Be Wary of Unknown Applications:** Only download apps from trusted sources, and review permissions before installation.
By implementing these best practices, individuals and organizations can significantly reduce their vulnerability to Android banking malware.
Key Takeaways
- ToxicPanda 2.0 and GoldDigger are sophisticated Android banking malware targeting financial data.
- Both malware variants employ advanced techniques like on-device fraud and social engineering.
- Businesses face significant risks, including financial losses and reputational damage, if they fail to address these threats.
- Proactive cybersecurity measures are essential for protecting against emerging threats.
Frequently Asked Questions
What should I do if I suspect my device has been infected?
If you suspect that your device is infected with malware like ToxicPanda 2.0 or GoldDigger, the first step is to disconnect from the internet to prevent any unauthorized access to your financial accounts. Next, run a complete scan using a reputable antivirus program to identify and remove any malicious software. If you notice any unauthorized transactions, immediately contact your bank and change your passwords.
How can businesses safeguard against these types of malware?
Businesses can safeguard against Android banking malware by implementing comprehensive cybersecurity policies that include regular software updates, employee training on recognizing phishing attempts, and the use of advanced security tools like intrusion detection systems. Establishing clear protocols for responding to suspected breaches is also critical for minimizing damage.
Are there specific signs that indicate my banking app has been compromised?
Signs that your banking app may have been compromised include unusual transaction activity, notifications of changes to account settings that you did not initiate, and unexpected prompts for additional authentication. If you notice any of these signs, it's crucial to take immediate action to secure your account and investigate further.
What is the future outlook for Android banking malware?
The future of Android banking malware is likely to see continued evolution and sophistication. As mobile banking becomes more prevalent, so too will the methods employed by cybercriminals. This underscores the need for ongoing vigilance, innovation in security technologies, and a commitment to user education to keep pace with emerging threats.
Comments
Castelion: The $13 Billion Startup Revolutionizing Hypersonic Weaponry
Castelion, a new player in the defense sector, has achieved a remarkable $13 billion valuation after securing a $1 billion Series C funding round. Founded by ex-SpaceX executives, the startup aims to transform hypersonic missile production, addressing critical military needs amidst rising global tensions.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation