Understanding the CDN Tsunami Attack: A Deep Dive into HTTP/3 Vulnerabilities
The recent CDN Tsunami attack highlights significant vulnerabilities in HTTP/3, showcasing potential amplification factors. This article explores the implications for businesses and cybersecurity strategies.
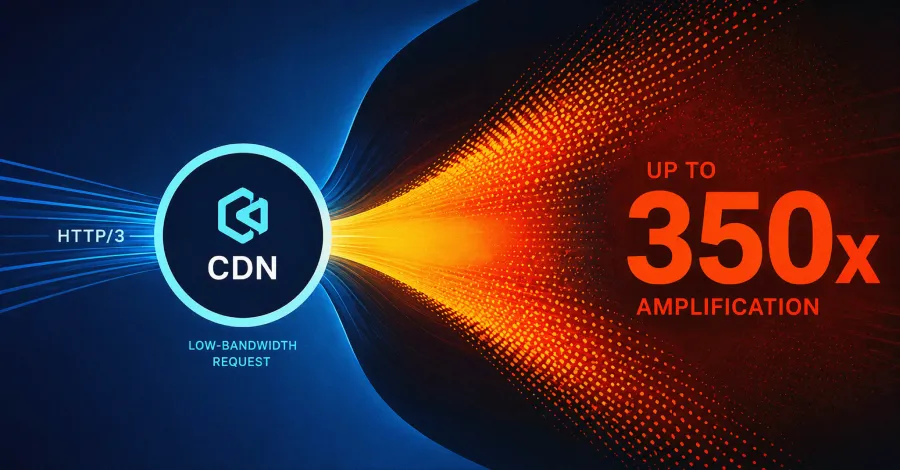
The world of web hosting and cloud infrastructure is constantly evolving, with new technologies promising faster, more efficient, and secure ways to deliver content. However, with innovation comes risk, as demonstrated by the recent CDN Tsunami attack. This incident has unveiled profound vulnerabilities in the HTTP/3 protocol, allowing for a staggering up to 350x amplification of Distributed Denial of Service (DDoS) attacks. Understanding the mechanics behind this attack not only sheds light on the security risks associated with emerging technologies but also underscores the necessity for businesses to adopt robust cybersecurity strategies.
As Content Delivery Networks (CDNs) increasingly leverage HTTP/3 for its speed and efficiency benefits, the implications of this vulnerability extend across the landscape of web infrastructure. Businesses relying on these technologies must stay informed and proactive in their defense against potential exploits that could severely disrupt their operations and data integrity.
Understanding HTTP/3 and Its Implications
HTTP/3, the latest iteration of the Hypertext Transfer Protocol, is built on QUIC (Quick UDP Internet Connections), which is designed to reduce latency and improve performance over the web. Unlike its predecessors, HTTP/3 operates over UDP rather than TCP, allowing for quicker connections and faster data transfers. However, this shift also introduces new vulnerabilities, particularly around how data is transmitted and received.
The CDN Tsunami attack specifically exploits this shift to amplify DDoS attacks. By leveraging the characteristics of HTTP/3, attackers can manipulate the protocol to create enormous volumes of traffic directed at a target, overwhelming their resources and causing service outages. This amplification factor can lead to up to 350 times the original request volume, turning a small-scale request into a massive flood of unwanted traffic.
The Mechanics of the CDN Tsunami Attack
The CDN Tsunami attack functions through a series of steps that exploit the nuances of HTTP/3's design. Attackers initiate the process by sending small request packets to a vulnerable CDN that translates HTTP/3 requests into traditional HTTP/2 or HTTP/1.1 requests. This translation process is where the amplification occurs. The CDN responds to these requests, generating much larger responses that are then sent to the target, resulting in a surge of traffic.
Here’s a simplified breakdown of the attack flow:
- Step 1: The attacker sends a small packet to the CDN.
- Step 2: The CDN processes the request and sends back a larger response.
- Step 3: The response is directed at the victim's server, overwhelming it with traffic.
This method of attack not only poses a risk to individual businesses but also threatens the stability of broader internet infrastructure. As more organizations adopt HTTP/3, the potential for similar attacks increases, highlighting a critical need for awareness and preparedness in the cybersecurity landscape.
Real Stories: Identity Exposure and Attack Paths
In addition to the vulnerabilities exposed by the CDN Tsunami attack, there are broader implications around identity exposure and cross-domain privilege escalation in the realm of cybersecurity. Recent studies have revealed how compromised identities can unlock active attack paths, enabling adversaries to navigate through systems and access sensitive data.
Consider the following scenarios:
- Privileged Access Abuse: An attacker gains unauthorized access to user credentials that allow them to escalate privileges within a system, navigating to sensitive data.
- Cross-Domain Attacks: Attackers exploit vulnerabilities in one domain to access resources in another, effectively bypassing security measures.
- Data Exfiltration: Once inside a system, attackers can siphon off valuable data, leading to financial losses and reputational damage.
These real-world stories illustrate the importance of robust identity management and security protocols. Organizations must implement stringent access controls and continuous monitoring to detect any unauthorized access attempts and mitigate potential breaches.
Implications for Businesses and Cybersecurity Strategies
The CDN Tsunami attack and the risks associated with identity exposure serve as a wake-up call for businesses across sectors. With the rise of cloud infrastructure and reliance on CDNs, organizations must reassess their cybersecurity strategies to address these vulnerabilities effectively.
To protect against the threats posed by the CDN Tsunami attack, businesses should consider the following strategies:
- Adopt a Zero Trust Model: Implement a security framework that assumes threats could be present both inside and outside the network, requiring verification for every access request.
- Regular Security Audits: Conduct frequent assessments of systems and protocols to identify vulnerabilities and ensure compliance with best practices.
- Educate Employees: Provide training on security awareness, including phishing attacks and the importance of safeguarding credentials.
- Utilize Advanced Threat Detection: Employ AI-driven security tools that can monitor traffic patterns and identify anomalies that may indicate an attack.
By taking proactive measures and fostering a culture of security awareness, businesses can better defend against the evolving landscape of cyber threats.
Key Takeaways
- The CDN Tsunami attack highlights critical vulnerabilities in HTTP/3, enabling DDoS amplification.
- Understanding the attack mechanics is essential for businesses relying on CDNs.
- Identity exposure poses significant risks, unlocking potential attack paths.
- Robust cybersecurity strategies are crucial for mitigating these vulnerabilities.
Frequently Asked Questions
What is HTTP/3 and why is it significant?
HTTP/3 is the latest version of the Hypertext Transfer Protocol, designed to improve web performance through faster data transmission over UDP. Its significance lies in its potential to enhance user experience on the internet, but it also introduces new vulnerabilities that can be exploited by attackers.
How can businesses protect themselves from DDoS attacks?
Businesses can protect themselves from DDoS attacks by implementing a combination of strategies, including adopting a Zero Trust security model, conducting regular security audits, and utilizing advanced threat detection tools. Additionally, organizations should ensure their CDNs are configured properly to mitigate amplification risks.
What role does identity management play in cybersecurity?
Identity management is crucial in cybersecurity as it controls user access to sensitive data and systems. Proper identity management reduces the risk of unauthorized access and helps organizations detect potential breaches before they escalate into significant incidents.
Are there specific industries more vulnerable to these types of attacks?
While all industries are susceptible to DDoS attacks and identity exposure, sectors such as finance, healthcare, and e-commerce are particularly vulnerable due to the sensitive nature of their data and the potential for significant financial loss during an attack.
Comments
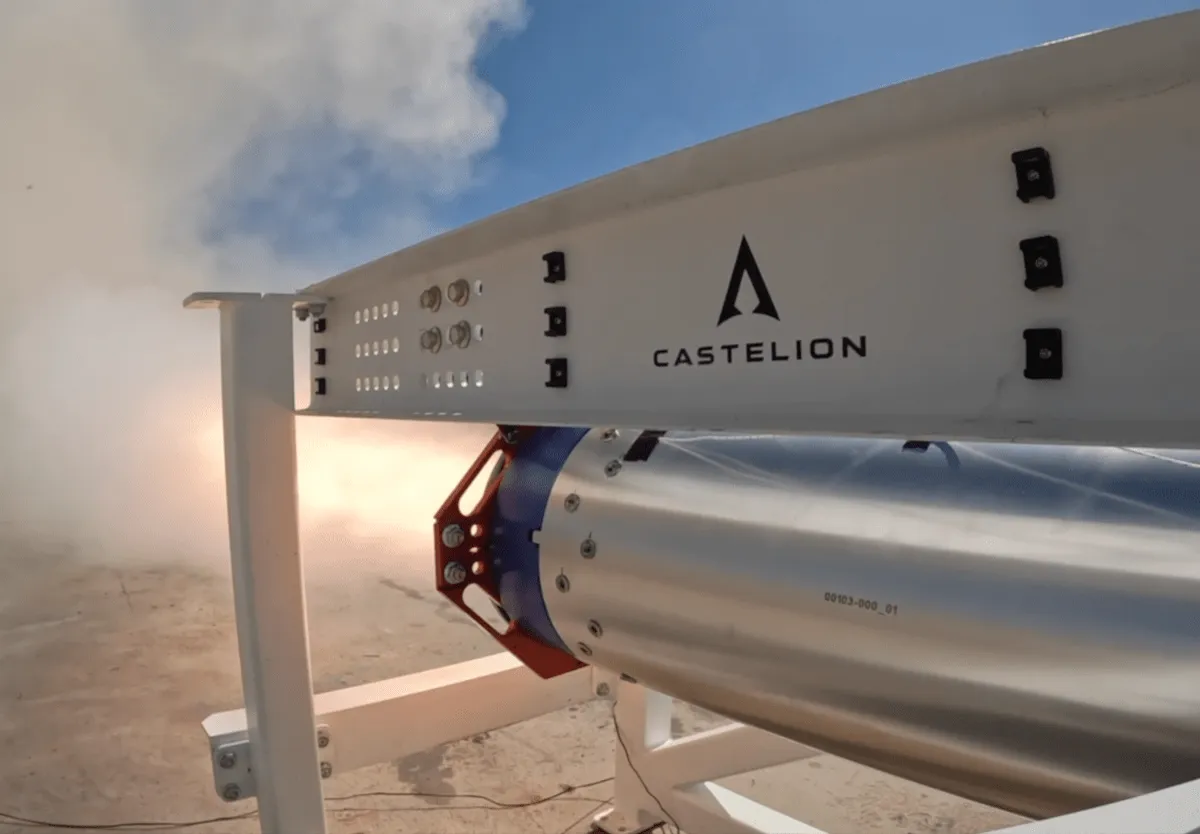
Castelion: The $13 Billion Startup Revolutionizing Hypersonic Weaponry
Castelion, a new player in the defense sector, has achieved a remarkable $13 billion valuation after securing a $1 billion Series C funding round. Founded by ex-SpaceX executives, the startup aims to transform hypersonic missile production, addressing critical military needs amidst rising global tensions.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation