Confronting Shady AI: The New Frontier in Security Governance
As artificial intelligence evolves, so do the risks associated with identity exposure and privilege escalation. Organizations must adapt their governance frameworks to tackle these emerging threats effectively.
As artificial intelligence (AI) systems become more integrated into business processes, they also introduce complex security challenges that organizations must confront. The rise of what some experts are calling "Shady AI" highlights the potential risks associated with identity exposure and cross-domain privilege escalation. With real-world stories illustrating how these vulnerabilities can be exploited, the need for robust governance frameworks is clearer than ever.
In a world increasingly reliant on AI solutions, organizations are tasked with not only harnessing the power of these technologies but also ensuring they do not become vectors for cyberattacks. The consequences of failing to manage these risks can be severe, leading to data breaches, financial loss, and reputational damage. In this article, we will explore the implications of Shady AI, along with strategies for mapping and mitigating these new attack vectors.
Understanding Shady AI and Its Implications
Shady AI refers to the misuse or malicious application of artificial intelligence technologies, particularly in ways that compromise security frameworks. This can involve anything from using AI to generate deepfakes for social engineering attacks to exploiting vulnerabilities in AI models that handle sensitive data.
Identity Exposure: A Growing Concern
As organizations adopt AI, they often expose identities unwittingly. For example, AI systems that aggregate data from various sources can inadvertently reveal personal information if not properly secured. Identity exposure not only threatens individual privacy but also creates pathways for attackers to escalate privileges within the organization.
- Increased attack surface: AI systems often interact with multiple platforms, potentially exposing sensitive data.
- Privilege escalation: Attackers can exploit identity access to gain higher-level permissions.
- Data breaches: Compromised identities can lead to significant data leaks.
Real-World Impacts: Stories of Exploitation
Numerous cases illustrate how identity exposure has led to active attack paths within organizations. For instance, one company found that an AI-driven tool meant to streamline customer service inadvertently exposed employee credentials through its integration with a third-party application. This breach allowed hackers to access sensitive company data, resulting in a costly recovery process and damage to the company’s reputation.
Mapping Cross-Domain Privilege Escalation
Understanding how attackers can navigate through an organization’s defenses is critical. Cross-domain privilege escalation allows malicious actors to leverage access gained from one domain to infiltrate others. This kind of mapping can identify choke points where organizations can sever breach routes before they are exploited.
Organizations should engage in regular assessments of their access controls and privilege management systems to ensure that they are not inadvertently facilitating these types of attacks. Mapping out potential escalation paths can provide a clearer picture of vulnerabilities and help prioritize remediation efforts.
Governance Frameworks: Adapting to New Threats
To effectively combat the risks associated with Shady AI, organizations must adapt their governance frameworks. This involves integrating AI risk assessments into existing security protocols, training employees on the unique challenges posed by AI technologies, and developing incident response plans tailored to AI-related breaches.
Key Components of an Effective Governance Strategy
1. **Risk Assessment**: Regularly evaluate AI systems for vulnerabilities and potential exposure points.
2. **Employee Training**: Conduct workshops to educate staff about the implications of AI misuse.
3. **Incident Response**: Create a plan specifically for addressing AI-related security incidents, ensuring quick and effective action.
4. **Third-Party Management**: Assess the security practices of vendors and partners who interact with your AI systems, ensuring they uphold stringent security measures.
Moving Forward: Proactive Measures for Organizations
As we look to the future, organizations must take proactive measures to mitigate the risks associated with Shady AI. This includes investing in advanced security technologies, such as AI-driven threat detection systems, which can help identify and respond to threats in real-time. Additionally, establishing a culture of security awareness can empower employees to identify potential vulnerabilities and report suspicious activities.
Collaboration and Information Sharing
Organizations should consider collaborating with industry peers to share insights and strategies for combatting AI-related security threats. Participating in forums and working groups can foster a community approach to tackling these challenges, ultimately leading to a more secure environment for all.
Key Takeaways
- Shady AI presents new security risks that organizations must address, particularly concerning identity exposure.
- Cross-domain privilege escalation can allow attackers to navigate through defenses, necessitating effective mapping and mitigation strategies.
- Integrating AI risk assessments into existing governance frameworks is essential for modern security management.
- Proactive measures, including employee training and collaboration, are critical in combating emerging threats.
Frequently Asked Questions
What is Shady AI?
Shady AI refers to the malicious or improper use of artificial intelligence technologies, particularly in ways that can lead to security vulnerabilities. This term encompasses various threats, including identity exposure and privilege escalation, which organizations must address to protect their data and systems.
How can organizations combat identity exposure?
Organizations can combat identity exposure by implementing robust access controls, regularly auditing their systems, and providing employee training on data privacy and security best practices. Additionally, engaging in threat modeling can help identify potential vulnerabilities and areas for improvement.
What role does employee training play in security governance?
Employee training is crucial in security governance as it helps create awareness of potential threats and empowers staff to recognize and report suspicious activities. Training programs should focus on the unique challenges posed by AI technologies and the importance of maintaining data security.
Why is collaboration important in addressing AI security threats?
Collaboration allows organizations to pool knowledge, share best practices, and develop comprehensive strategies for combatting AI-related security threats. By working together, organizations can enhance their overall security posture and contribute to a safer digital environment.
Comments
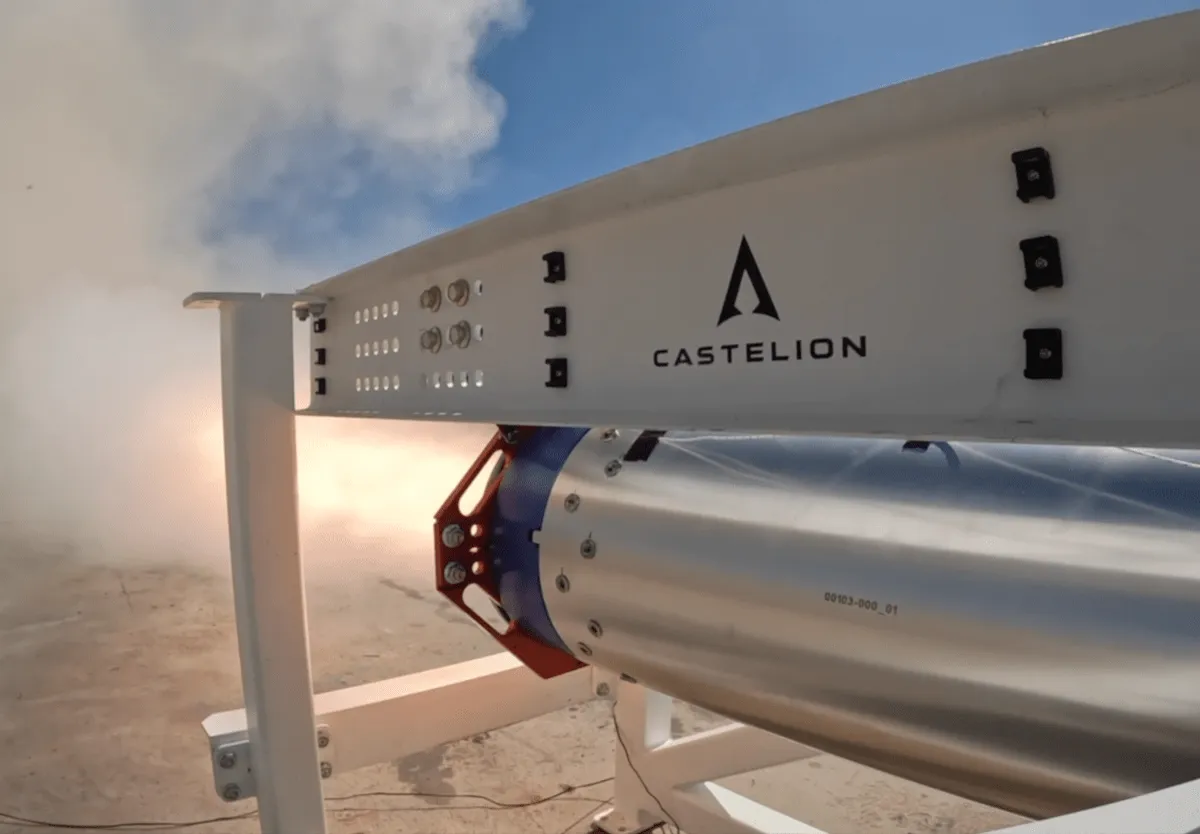
Castelion: The $13 Billion Startup Revolutionizing Hypersonic Weaponry
Castelion, a new player in the defense sector, has achieved a remarkable $13 billion valuation after securing a $1 billion Series C funding round. Founded by ex-SpaceX executives, the startup aims to transform hypersonic missile production, addressing critical military needs amidst rising global tensions.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation