Inside the Deceptive World of Cybersecurity: A Fake Crypto Startup and Its Lessons
In a groundbreaking experiment, researchers created a fake cryptocurrency startup and hired suspected North Korean IT workers to reveal vulnerabilities in cybersecurity practices. This article delves into the implications of such tactics for businesses and the broader cybersecurity landscape.
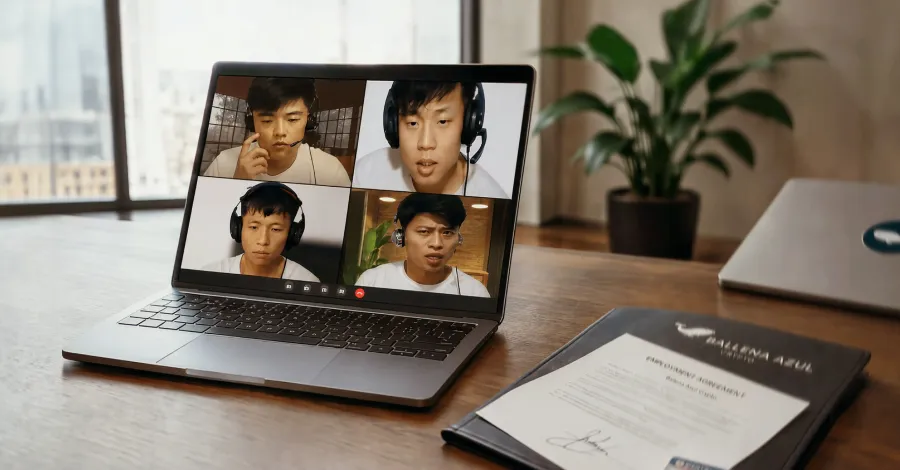
In the fast-evolving world of cybersecurity, deception is becoming an increasingly vital strategy. Recent research conducted by cybersecurity experts involved the creation of a fake cryptocurrency startup, which was designed to expose vulnerabilities within the industry. By hiring three suspected North Korean IT workers, the researchers aimed to shed light on the risks that organizations face when it comes to identity exposure and cyber threats. This innovative approach not only underscores the sophistication of cybercriminal tactics but also highlights the urgent need for businesses to reassess their security measures.
The Motivation Behind the Experiment
As cryptocurrency continues to gain traction, it has become a lucrative target for cybercriminals. The allure of anonymous transactions and the potential for massive financial gain make it an attractive space for malicious actors. Researchers sought to understand how easily a fake entity could be infiltrated and exploited, especially when staffed by individuals with questionable backgrounds. The experiment aimed to simulate real-world scenarios that companies might face, thereby providing a clearer picture of the cybersecurity landscape.
Understanding the Actors: North Korean IT Workers
The involvement of suspected North Korean IT workers adds a fascinating layer to the narrative. North Korea has long been associated with cyberattacks, with groups like Lazarus and APT38 being notorious for their sophisticated hacking capabilities. By hiring individuals linked to such organizations, researchers intended to understand how these actors operate within the frameworks of legitimate businesses.
The Skillset of Cybercriminals
Those engaged in cybercrime often possess a unique skill set, including:
- Advanced Technical Knowledge: Proficiency in programming and network systems.
- Social Engineering Skills: The ability to manipulate individuals into divulging confidential information.
- Resourcefulness: Utilizing diverse tools and techniques to exploit vulnerabilities.
- Adaptability: Quickly evolving tactics in response to security measures.
Understanding these skills is crucial for organizations looking to defend against similar threats.
Revealing Vulnerabilities Through Deception
The experiment's findings revealed several vulnerabilities that organizations must address to safeguard their operations:
Identity Exposure and Its Consequences
Identity exposure can lead to significant breaches, allowing attackers to map out cross-domain privilege escalations. This means that a compromised identity can serve as a gateway for further attacks, leading to potential breaches at critical chokepoints within an organization. The researchers emphasized the importance of monitoring and controlling access to sensitive information, as well as regularly assessing the security posture of both internal and external actors.
The Role of Continuous Security Assessment
Organizations must not only implement security measures but also engage in continuous assessment. This includes regular penetration testing, vulnerability scanning, and employee training on security best practices. The dynamic nature of cyber threats necessitates that businesses remain proactive in their defenses.
Best Practices for Organizations
Based on the insights garnered from the experiment, organizations should consider adopting a robust cybersecurity framework. Some recommended practices include:
- Implementing Zero Trust Architecture: This approach requires strict identity verification for every person and device attempting to access resources.
- Utilizing Multi-Factor Authentication (MFA): MFA adds an additional layer of security, making unauthorized access more difficult.
- Conducting Regular Security Audits: These audits help identify potential weaknesses and ensure compliance with security policies.
- Investing in Employee Training: Regular training can empower employees to recognize and respond to potential threats.
Key Takeaways
- The creation of a fake cryptocurrency startup demonstrates the ease with which cybercriminals can infiltrate organizations.
- Identity exposure significantly increases the risk of cyberattacks, particularly from sophisticated actors.
- Continuous security assessment and employee training are essential components of a strong cybersecurity posture.
- Implementing best practices such as Zero Trust and MFA can help organizations defend against evolving threats.
Frequently Asked Questions
What is the significance of using a fake startup in cybersecurity research?
The use of a fake startup allows researchers to simulate realistic scenarios that organizations might encounter in the wild. It provides valuable insights into vulnerabilities and the tactics employed by cybercriminals without compromising real businesses.
How can organizations protect themselves from identity exposure?
Organizations can protect themselves by implementing strict access controls, monitoring user activities, and regularly reviewing security protocols. Investing in technologies like identity and access management (IAM) systems can also be beneficial in mitigating risks associated with identity exposure.
What role does employee training play in cybersecurity?
Employee training is crucial in creating a security-aware culture within an organization. Regular training sessions can help employees recognize phishing attempts, social engineering tactics, and other common threats, thereby reducing the likelihood of successful attacks.
Why is continuous security assessment important?
Continuous security assessment is vital because the landscape of cyber threats is constantly evolving. Regular assessments help organizations identify new vulnerabilities and adapt their security measures accordingly, ensuring they remain one step ahead of potential attackers.
Comments
How Supply Chain Attacks Compromise WordPress Security: A Case Study
A recent supply chain attack targeting BdThemes highlights the vulnerabilities within WordPress plugins. This article explores the impact, implications, and preventive measures for businesses.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation