Beware of Typosquatting: RubyGems Packages Targeting Your Credentials
Typosquatting poses a significant threat to developers and users alike, with malicious RubyGems packages designed to steal sensitive information. Understanding this risk is crucial in today’s digital landscape.
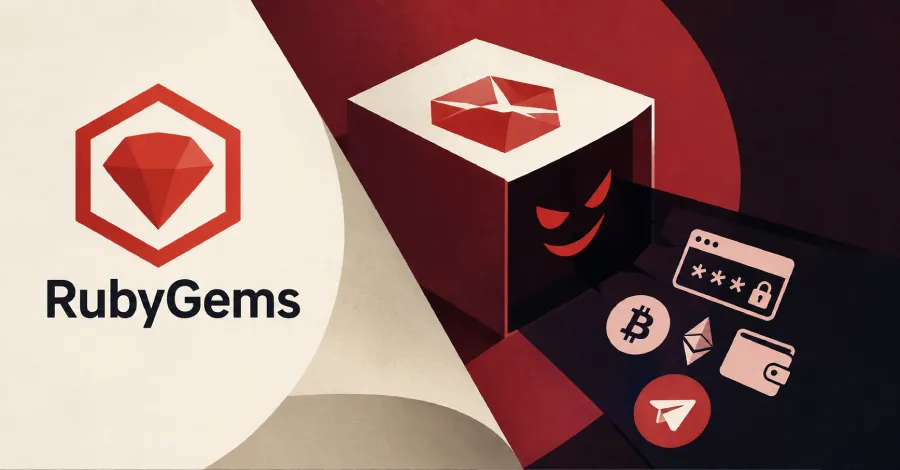
In the fast-paced world of software development, the rise of typosquatting has become an alarming trend that poses a serious threat to developers and end-users alike. Typosquatting involves creating malicious packages that mimic legitimate ones, often with minor spelling errors, enticing unsuspecting users to download them. Recently, security researchers identified 16 such typosquatted RubyGems packages that are specifically designed to steal sensitive information, including browser credentials and cryptocurrency wallet details. This article delves into the implications of typosquatting, how it operates, and what developers and users can do to protect themselves.
Understanding Typosquatting in the Software Ecosystem
Typosquatting is a form of cyber deception where attackers register domain names or software packages that closely resemble legitimate ones but contain slight misspellings or variations. This tactic exploits typographical errors made by users who are searching for popular libraries or tools. In the context of RubyGems, a popular package manager for the Ruby programming language, attackers create similar package names that can easily confuse developers during the installation process.
The 16 identified RubyGems packages are a stark reminder of how such tactics can lead to severe security breaches. Once downloaded and executed, these malicious packages can harvest sensitive information stored in users’ browsers or crypto wallets. Because many developers rely on RubyGems for essential libraries, the risk of inadvertently installing a compromised package is alarmingly high.
How Typosquatting Works: The Mechanics of Deception
To understand the mechanics of typosquatting, we must look at the lifecycle of package installation and the reliance on community trust. When developers use RubyGems, they typically type in the package name they wish to install. For instance, if they intend to install a reputable package like 'rails', a simple typo such as 'rail' can lead them to a malicious version.
The Attack Vector
Once users install a typosquatted package, the code within may execute malicious scripts designed to:
- Steal browser credentials: These scripts can access stored passwords and login sessions, allowing attackers to hijack user accounts.
- Extract crypto wallet data: Attackers can gain access to cryptocurrency wallets, leading to potential financial losses.
- Establish backdoors: Some packages may create hidden pathways for attackers to exploit the system further.
These threats underline the importance of vigilance among developers when selecting packages for their projects. The unique nature of open-source software, which emphasizes collaboration and trust, also opens the door for exploitation through typosquatting.
The Impact on Developers and Organizations
The consequences of typosquatting can be dire for both individual developers and organizations. For developers, falling victim to a typosquatted package can result in:
- Data theft: Loss of sensitive information can lead to compromised accounts and loss of intellectual property.
- Reputation damage: Developers may suffer from a loss of credibility if their projects are associated with security breaches.
- Financial implications: If an organization is compromised, it can face significant financial losses, regulatory scrutiny, and legal ramifications.
Organizations that rely on third-party libraries must maintain a robust security posture, including regular audits of dependencies and implementing strict package validation protocols. Failing to do so can open doors to active attack paths and severe breaches.
Mitigating the Risks: Best Practices for Developers
To protect against the dangers of typosquatting, developers should adopt a proactive approach to package management. Here are several best practices:
- Verify package integrity: Always check the package source and author. Use tools that verify the integrity of packages before installation.
- Utilize dependency management tools: Tools like Bundler can help manage dependencies and ensure that only trusted packages are used.
- Stay informed: Regularly monitor security advisories related to RubyGems and other package managers to stay updated on vulnerabilities.
- Educate teams: Conduct training sessions on identifying phishing attempts and recognizing suspicious packages.
By implementing these measures, developers can significantly reduce the risk of falling victim to typosquatting and protect their projects from malicious exploitation.
Key Takeaways
- Typosquatting in RubyGems packages poses significant security risks, including data theft and financial losses.
- Developers must remain vigilant when installing packages, ensuring they verify sources and integrity.
- Implementing best practices and utilizing dependency management tools can mitigate risks associated with typosquatting.
- Regular education and awareness programs can help teams recognize and avoid potential threats.
Frequently Asked Questions
What should I do if I suspect I've installed a typosquatted package?
If you suspect that you have installed a typosquatted package, immediately uninstall it and conduct a thorough security audit of your project. Check for any unauthorized changes to your code or systems and monitor for any suspicious activity in your accounts. Additionally, consider changing passwords and enabling two-factor authentication for any affected accounts.
How can I identify legitimate packages on RubyGems?
To identify legitimate packages on RubyGems, look for packages that have a high number of downloads, positive user reviews, and are maintained by reputable authors or organizations. You can also check for the presence of documentation, regular updates, and community engagement. Additionally, tools that verify package integrity can assist in ensuring you are using trusted packages.
Are there specific tools I can use to prevent typosquatting attacks?
Yes, several tools can help prevent typosquatting attacks. Dependency management tools like Bundler help manage and track package installations, while security scanners can automatically detect vulnerabilities in your dependencies. Additionally, using static analysis tools can help identify potential issues in the code before deployment.
Comments
OpenAI Reinforces Security Measures Following Hugging Face Breach
In response to increasing risks associated with AI model development, OpenAI has unveiled new security protocols aimed at enhancing monitoring and safeguarding practices. These changes come on the heels of the Hugging Face breach, prompting a reevaluation of how AI models are tested and monitored.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation