Exploiting Zero-Day Vulnerabilities: A Deep Dive into Microsoft Defender Bypass and Identity Exposure
Recent reports have unveiled a significant zero-day vulnerability in Microsoft Defender that allows attackers to bypass security measures and gain SYSTEM access. This article explores the implications of such vulnerabilities and how they can facilitate identity exposure, leading to active attack paths.
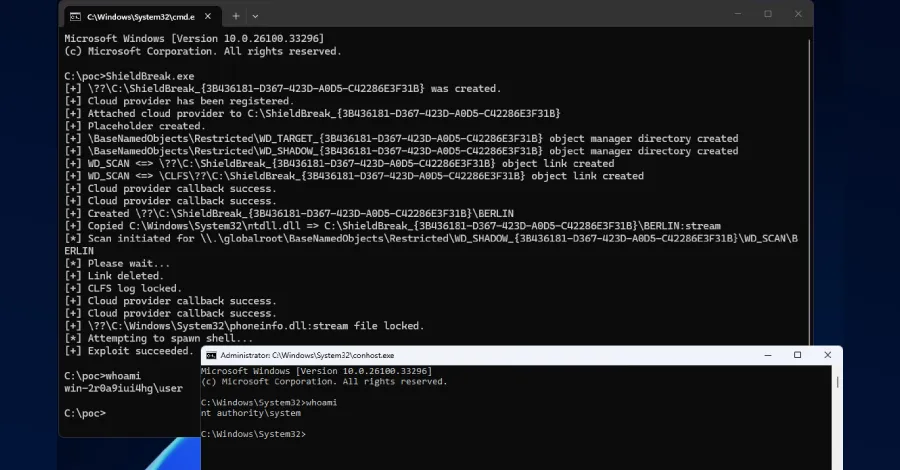
In the increasingly complex landscape of cybersecurity, the emergence of zero-day vulnerabilities poses significant threats to organizations relying on software like Microsoft Defender. A recent proof of concept (PoC) has demonstrated a bypass of Microsoft Defender's defenses, allowing attackers to gain SYSTEM-level access. This vulnerability not only puts systems at risk but also highlights how identity exposure can unlock active attack paths within networks, leading to potentially devastating breaches.
As organizations strive to protect their digital assets, understanding the implications of such vulnerabilities and taking proactive measures is essential. This article delves deep into the technical aspects of the Microsoft Defender bypass, explores real-world instances of identity exposure, and outlines steps that organizations can take to mitigate these risks.
The Microsoft Defender Vulnerability: An Overview
Microsoft Defender, a critical component of Windows security, is designed to protect against malware and other threats. However, the discovery of a zero-day vulnerability that enables attackers to bypass these protections raises alarms in the cybersecurity community. Zero-day vulnerabilities refer to security flaws that developers are unaware of, leaving systems open to exploitation until a patch is released.
The PoC indicating the bypass of Microsoft Defender was shared by cybersecurity researchers, illustrating how attackers can leverage this vulnerability to execute arbitrary code with SYSTEM privileges. This level of access allows them to control the affected system completely, potentially leading to data breaches, system manipulation, and further infiltration of the network.
Understanding Zero-Day Vulnerabilities
Zero-day vulnerabilities are particularly dangerous because they are exploited before the vendor has a chance to address them. This gives attackers a window of opportunity to deploy malware or conduct malicious activities without any defenses in place. The implications of such vulnerabilities extend beyond the immediate threat; they can also affect an organization’s reputation, customer trust, and compliance with regulations.
The Role of Identity Exposure in Cybersecurity
Identity exposure is another critical factor in the cybersecurity landscape. When sensitive personal information or credentials are compromised, it can lead to unauthorized access and privilege escalation within an organization. A recent study showed that over 80% of data breaches involved some form of identity exposure, highlighting the importance of securing user identities.
In the context of the Microsoft Defender vulnerability, identity exposure can amplify the risks. Once an attacker gains SYSTEM access, they can map out cross-domain privilege escalations, effectively unlocking multiple pathways for further attacks. This can create a cascading effect where a single breach can compromise an entire network.
Real-World Examples of Identity Exposure
To illustrate the dangers of identity exposure, consider the following scenarios:
- Credential Stuffing Attacks: Attackers use stolen usernames and passwords from one breach to gain access to accounts on other platforms.
- Social Engineering: Phishing attacks manipulate employees into providing sensitive information, leading to unauthorized access.
- Unsecured APIs: Exposed application programming interfaces can allow attackers to gain access to user data and escalate privileges.
These examples show how identity exposure can serve as a gateway for attackers, especially when combined with vulnerabilities like the one found in Microsoft Defender.
Mitigating Risks: Best Practices for Organizations
Given the potential for zero-day vulnerabilities and identity exposure to wreak havoc on organizations, it is crucial for businesses to adopt robust security measures. Here are several best practices that organizations should implement:
- Regular Software Updates: Ensure that all systems, including Microsoft Defender, are updated with the latest patches and security updates.
- Conduct Security Audits: Regular audits can help identify vulnerabilities and assess the effectiveness of current security measures.
- Implement Multi-Factor Authentication (MFA): Adding an extra layer of security can help protect accounts even if credentials are compromised.
- Employee Training: Educate employees about phishing attacks and the importance of safeguarding their credentials.
- Network Segmentation: Limit access to sensitive information based on user roles to minimize the impact of a breach.
Key Takeaways
- The recent zero-day vulnerability in Microsoft Defender allows attackers to gain SYSTEM access.
- Identity exposure is a significant risk, enabling unauthorized access and privilege escalation.
- Organizations must employ best practices, including regular updates and employee training, to mitigate risks.
- Understanding the connection between vulnerabilities and identity exposure is crucial for effective cybersecurity.
Frequently Asked Questions
What is a zero-day vulnerability?
A zero-day vulnerability is a security flaw that is unknown to the software vendor and, therefore, has not yet been patched. Attackers exploit these vulnerabilities before the vendor can release a fix, making them particularly dangerous. Organizations must remain vigilant and implement security measures to protect against such threats.
How can identity exposure lead to data breaches?
Identity exposure occurs when sensitive information or credentials are compromised, allowing unauthorized users to gain access to systems or data. This can lead to data breaches when attackers leverage exposed identities to escalate privileges and conduct malicious activities within an organization.
What steps can organizations take to protect against zero-day vulnerabilities?
Organizations can protect against zero-day vulnerabilities by maintaining regular software updates, conducting security audits, implementing multi-factor authentication, and training employees to recognize potential threats. These proactive measures can help minimize the risk of exploitation.
Why is employee training important in cybersecurity?
Employee training is essential in cybersecurity because human error is often a leading cause of data breaches. Educating employees about security best practices, how to recognize phishing attempts, and the importance of safeguarding their credentials can significantly reduce the risk of identity exposure and breaches.
Comments
Critical Cisco ASA and FTD Vulnerability: Understanding the Risks
A recently discovered vulnerability affecting Cisco's ASA and FTD devices has been exploited in the wild, triggering remote Denial of Service (DoS) attacks. This article explores the implications for businesses and how they can mitigate risks.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation