DeadLock Ransomware: The New Frontier of Cyber Extortion
The DeadLock ransomware exemplifies a new wave of cyber extortion, utilizing blockchain technology to complicate disruption efforts. This article explores its implications for cybersecurity and business resilience.
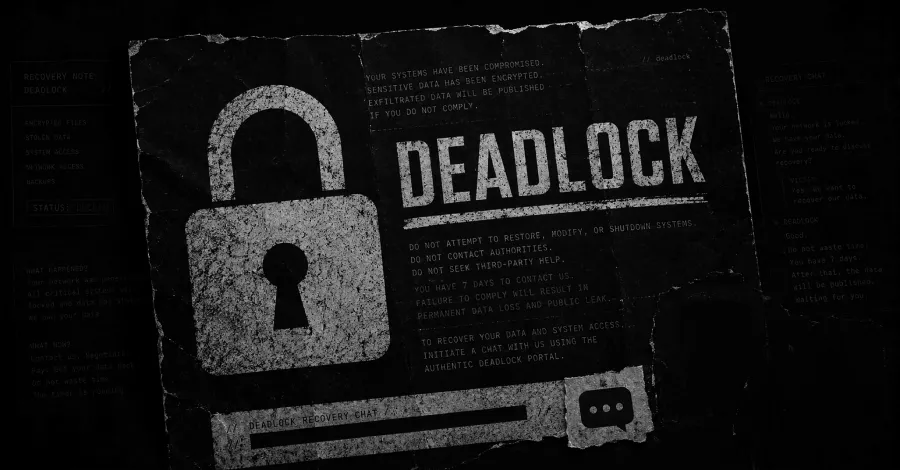
In an era where cyber threats evolve at lightning speed, the emergence of DeadLock ransomware marks a significant turning point in the landscape of cyber extortion. Unlike traditional ransomware, which typically operates on a straightforward model of encrypting data and demanding a ransom for decryption keys, DeadLock leverages Polygon's smart contract technology to create a decentralized and more resilient extortion framework. This transformation not only complicates law enforcement efforts but also raises the stakes for businesses aiming to safeguard their data and maintain operational integrity.
The implications of DeadLock's innovative approach are profound. By utilizing smart contracts, the ransomware can execute payment collection automatically, making it challenging for victims to trace and disrupt the extortion process. Furthermore, the use of blockchain technology introduces an element of anonymity and security for the perpetrators, complicating recovery efforts. As organizations grapple with these evolving threats, it becomes imperative to understand the mechanics behind this ransomware and implement robust cybersecurity defenses.
Understanding DeadLock Ransomware
DeadLock ransomware operates on the principles of decentralization and automation, utilizing the Polygon blockchain to enhance its extortion capabilities. In traditional ransomware schemes, attackers would typically demand payment in cryptocurrencies like Bitcoin, which, while offering a degree of anonymity, can still be tracked through various blockchain analysis techniques. DeadLock, however, takes it a step further by embedding payment protocols directly into smart contracts.
The Mechanics of Smart Contracts
Smart contracts are self-executing contracts with the terms of the agreement directly written into code. They run on blockchain networks and facilitate, verify, or enforce the negotiation or performance of a contract. In the case of DeadLock:
- Automated Transactions: Payments made to the attackers can be automatically recorded and processed, minimizing the need for human intervention.
- Anonymity: The decentralized nature of blockchain ensures that the identities of the attackers remain obscured.
- Irreversibility: Once a transaction is executed, it cannot be undone, making it difficult for victims to reclaim their funds.
The Impact on Businesses and Cybersecurity
The rise of DeadLock ransomware signifies a shift in the threat landscape that businesses must navigate. As organizations increasingly adopt digital transformation strategies, they inadvertently expose themselves to a wider range of vulnerabilities. With ransomware like DeadLock, the attack surface broadens, and traditional cybersecurity measures may no longer suffice.
Vulnerabilities Exposed
With the introduction of smart contract-based ransomware, businesses face several critical vulnerabilities:
- Cross-Domain Privilege Escalation: Attackers can exploit weaknesses across different systems, allowing them to elevate their access and control over sensitive data.
- Supply Chain Risks: As more companies rely on third-party vendors, ransomware can traverse through interconnected systems, amplifying the impact of an attack.
- Data Integrity Challenges: The decentralized nature of blockchain can complicate data recovery, making it harder for organizations to restore operations after an attack.
Strategies for Mitigating Risks
Given the increasing sophistication of ransomware attacks, organizations must adopt a multi-faceted approach to cybersecurity. Here are key strategies to consider:
1. Implement Comprehensive Security Protocols
Organizations should evaluate and enhance their security measures, including:
- Regular software updates and patch management.
- Multi-factor authentication (MFA) to secure access to sensitive systems.
- Employee training on identifying phishing attempts and other social engineering attacks.
2. Develop an Incident Response Plan
An effective incident response plan is crucial for minimizing the damage from a ransomware attack. This plan should include:
- Clear communication protocols for internal and external stakeholders.
- Steps for isolating infected systems to prevent further spread.
- Engagement with cybersecurity experts to assess and mitigate the attack.
Key Takeaways
- DeadLock ransomware utilizes smart contracts on the Polygon blockchain, complicating disruption efforts.
- Traditional cybersecurity measures may be inadequate against this emerging threat.
- Cross-domain privilege escalation and supply chain vulnerabilities are critical risks organizations must address.
- Implementing comprehensive security protocols and an incident response plan is essential for defense.
Frequently Asked Questions
What is DeadLock ransomware, and how does it differ from traditional ransomware?
DeadLock ransomware is a new type of cyber extortion that uses smart contracts on the Polygon blockchain to automate and obscure payment processes. Unlike traditional ransomware that relies on direct payment requests, DeadLock's use of smart contracts complicates recovery and tracking efforts, making it a more resilient method of extortion.
How can businesses protect themselves from ransomware like DeadLock?
Businesses can protect themselves by implementing robust cybersecurity measures, including regular updates and patches, multi-factor authentication, and comprehensive employee training programs. Additionally, developing an incident response plan is critical for quickly addressing any potential attacks.
What role do smart contracts play in ransomware attacks?
Smart contracts play a significant role in modern ransomware attacks by automating payment collection and enhancing anonymity for attackers. This technology enables seamless, irreversible transactions that complicate law enforcement efforts to track and disrupt criminal activities.
Comments
Critical Cisco ASA and FTD Vulnerability: Understanding the Risks
A recently discovered vulnerability affecting Cisco's ASA and FTD devices has been exploited in the wild, triggering remote Denial of Service (DoS) attacks. This article explores the implications for businesses and how they can mitigate risks.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation