Exploiting VoLTE: Understanding the Unisoc Vulnerability and Its Implications
The recent Unisoc VoLTE exploit reveals critical vulnerabilities in Android devices that could allow attackers unprecedented access. This article dissects the exploit chain, its implications for users, and how to safeguard against such threats.
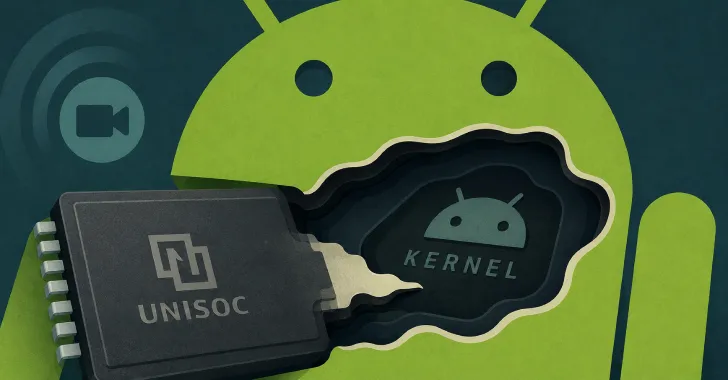
In a worrying development for mobile security, researchers have unveiled a sophisticated exploit chain associated with Unisoc's Voice over LTE (VoLTE) technology. This exploit grants attackers the potential to gain full access to the Android kernel, effectively compromising the integrity of devices running the affected chipsets. As VoLTE becomes a standard feature in modern smartphones, understanding the implications of this vulnerability for both consumers and enterprises is critical.
VoLTE technology is designed to enhance voice quality over LTE networks, but the recent findings indicate that its implementation may have introduced significant security flaws. With the ability to access the kernel, attackers can manipulate system-level functions, leading to severe consequences such as data theft, unauthorized access to applications, and even device bricking. This article explores the details of the exploit, its potential impact, and what steps users can take to mitigate risks.
Understanding the Unisoc VoLTE Vulnerability
The Unisoc VoLTE exploit is rooted in a series of vulnerabilities that allow for cross-domain privilege escalation. Essentially, this means that an attacker can exploit one part of the system to gain unauthorized access to another, more sensitive part. The attack chain starts with a compromised application or service that takes advantage of the vulnerabilities in VoLTE to escalate privileges and execute arbitrary code at the kernel level.
The Mechanism of Attack
At its core, the exploit leverages flaws in the way VoLTE handles video calls. By manipulating signaling messages during a call setup, an attacker can inject malicious code that ultimately leads to kernel access. This process can be broken down into several key steps:
- Step 1: The attacker initiates a VoLTE video call to the target device.
- Step 2: During the call setup, the attacker sends specially crafted signaling messages.
- Step 3: The target device's VoLTE stack processes these messages, leading to the execution of malicious code.
- Step 4: The malicious code escalates privileges, providing full access to the Android kernel.
Implications for Users and Enterprises
The ramifications of this vulnerability extend far beyond individual users. For enterprises that rely on Android devices for business operations, the potential for data breaches and unauthorized access to sensitive information presents a considerable risk. Attackers gaining kernel access could manipulate device settings, intercept communications, and extract confidential data without detection.
Furthermore, this exploit highlights the need for robust security measures in the development and deployment of mobile technologies. As VoLTE becomes increasingly prevalent, manufacturers must prioritize security to mitigate similar vulnerabilities in the future. The Unisoc incident serves as a stark reminder that even widely adopted technologies can harbor significant risks.
Mitigating Risks: Best Practices for Users
Given the severity of the Unisoc VoLTE exploit, users should take immediate action to secure their devices. Here are several best practices to follow:
- Keep Software Updated: Regularly check for and install updates for your device's operating system and applications to close any security gaps.
- Use Trusted Applications: Only download apps from reputable sources such as the Google Play Store, and avoid sideloading applications from unknown developers.
- Enable Security Features: Utilize built-in security features such as biometric authentication, app permissions, and remote wipe capabilities.
- Monitor Device Activity: Be vigilant about unusual activity on your device, such as unexplained battery drain or unfamiliar applications.
The Role of Manufacturers in Security
While users play a crucial role in securing their devices, manufacturers also bear significant responsibility. Companies like Unisoc must implement rigorous security protocols during the design and testing phases of their technologies. This includes:
- Conducting Comprehensive Security Audits: Regularly assess products for vulnerabilities before they reach the market.
- Establishing Rapid Response Teams: Create teams that can quickly address vulnerabilities as they are discovered.
- Increasing Transparency: Provide clear communication to users about potential risks and the measures taken to mitigate them.
Key Takeaways
- The Unisoc VoLTE exploit highlights significant vulnerabilities in Android devices.
- Attackers can potentially gain full kernel access through a series of privilege escalation steps.
- Users and enterprises must adopt security best practices to protect against exploits.
- Manufacturers need to take proactive measures to enhance security in their technologies.
Frequently Asked Questions
What is VoLTE and why is it important?
VoLTE, or Voice over LTE, is a technology that allows voice calls to be made over LTE networks rather than traditional circuit-switched networks. This results in improved call quality and faster connection times. As LTE networks become the standard for mobile communication, understanding the security implications of VoLTE is crucial for both consumers and enterprises.
How can I tell if my Android device is vulnerable?
To determine if your device is vulnerable, check for any announcements from your device manufacturer regarding security updates related to the Unisoc VoLTE exploit. Keeping your device's operating system and applications updated is the best way to ensure you have the latest security patches. You can also use security apps that scan for known vulnerabilities.
What should I do if I suspect my device has been compromised?
If you suspect that your device has been compromised, it is essential to take immediate action. Disconnect from any networks, perform a factory reset, and change your passwords for any sensitive accounts accessed from the device. Additionally, consider consulting a cybersecurity professional for a thorough analysis.
Comments
How MCP Servers Can Compromise Enterprise Security: Real Stories and Solutions
MCP servers can be a double-edged sword in enterprise environments, potentially exposing sensitive data. This article explores real-world incidents of identity exposure and offers strategies for mitigating risks.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation