Boston Scientific Faces Cyberattack, Disrupting Global Operations
Boston Scientific is grappling with a significant cyberattack that is disrupting its global operations, particularly affecting its critical IT systems. This incident raises serious concerns about cybersecurity in the medical device sector.
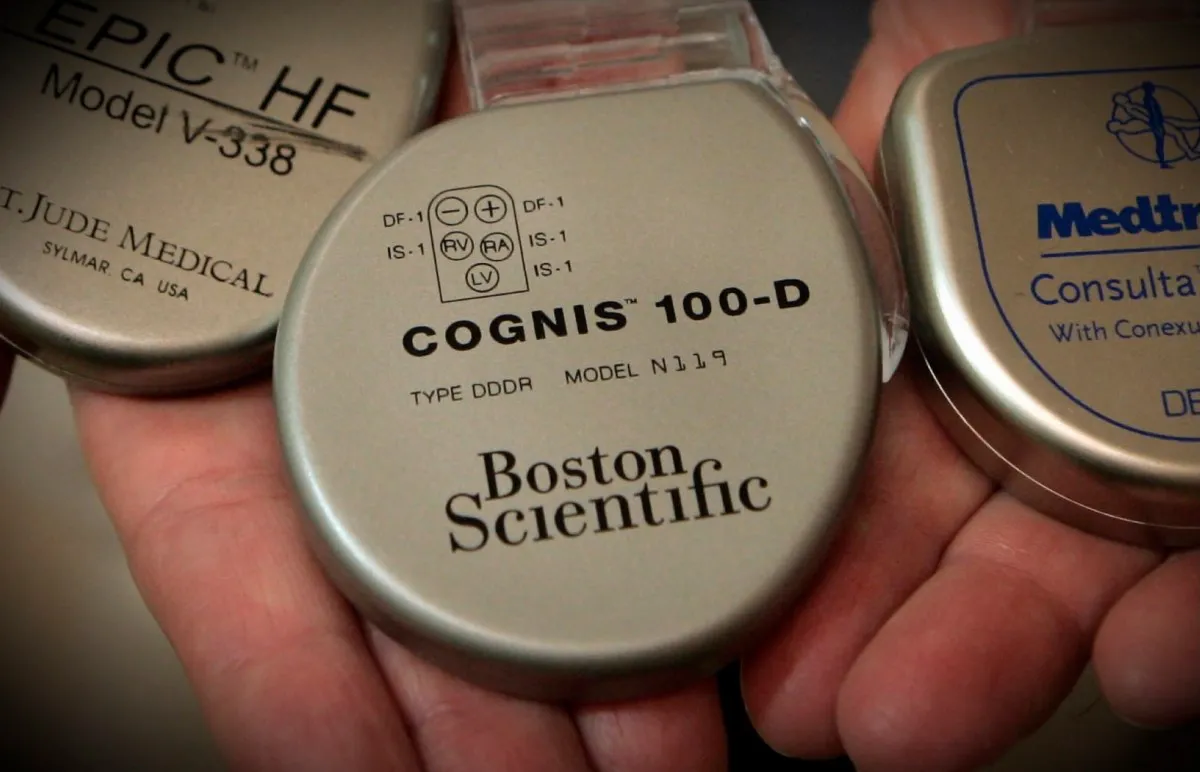
In a troubling development for the healthcare technology industry, Boston Scientific, a prominent U.S. medical device manufacturer, is currently reeling from a serious cyberattack that has led to widespread operational disruptions. Known for its range of medical devices, including pacemakers and defibrillators, Boston Scientific's incident is emblematic of a growing trend of cybersecurity breaches impacting health tech companies. The ramifications of this attack extend beyond the company itself, raising critical questions about patient safety, data security, and the integrity of medical technologies.
On August 26, 2026, Boston Scientific reported to the U.S. Securities and Exchange Commission (SEC) that it had begun experiencing significant limitations in access to its IT systems and business applications essential for daily operations. The disruption has affected the company’s ability to ship and process orders, further complicating its critical role in providing medical devices to healthcare facilities around the globe. The scale of the impact is still being assessed, but the company's statement suggests a serious level of operational impairment.
The Scope of the Cyberattack
Boston Scientific has confirmed that the cyberattack has led to a “global disruption” of its operations, although specific details about the nature of the attack remain scarce. The company indicated that it is actively investigating the incident but has not disclosed whether patient data has been compromised or if any patients have been directly affected. This lack of transparency has raised concerns among both patients and healthcare providers who rely on Boston Scientific's products.
The incident is particularly alarming given that Boston Scientific serves around 48 million patients annually. Patients depend on the reliability of implanted devices, and any disruption in the supply chain could pose serious health risks. As the company attempts to restore its systems, the timeline for resolution remains uncertain, leaving many questions unanswered.
The Broader Context: A Surge in Cyberattacks on Healthcare
This cyberattack on Boston Scientific is not an isolated incident. The healthcare sector has increasingly become a target for cybercriminals, with notable attacks occurring against other medical device manufacturers such as Abbott Laboratories and Medtronic earlier this year. For instance, in a previous incident, Iranian-backed hackers targeted Stryker, another medical device maker, using vulnerabilities in Microsoft’s device management portal to wipe thousands of employee devices. Such breaches highlight the vulnerabilities within the healthcare infrastructure and the urgent need for enhanced cybersecurity protocols.
Cybersecurity threats in healthcare can have catastrophic consequences. With patient safety at stake, it is imperative for companies to adopt comprehensive security measures. Cybercriminals often exploit the interconnected systems within healthcare organizations, making it easier to infiltrate networks and access sensitive data. The reliance on cloud services such as Microsoft Azure and Amazon Web Services for corporate infrastructure compounds these risks, as any vulnerabilities in these platforms can have far-reaching implications.
What This Means for Patients and Healthcare Providers
For patients, the implications of a cyberattack on a medical device manufacturer can be profound. The uncertainty surrounding the integrity of medical devices and the potential for supply chain disruptions raises significant concerns. Healthcare providers must be vigilant, ensuring that they have contingency plans in place to address any potential shortages or issues stemming from this incident.
Moreover, patients who rely on implanted devices may feel anxious about their safety and the reliability of their medical treatments. Boston Scientific has not yet confirmed whether any implants are affected, but the ambiguity around the situation is unsettling. Patients should remain informed and consult their healthcare providers for any specific guidance related to their medical devices during this period.
Key Lessons in Cybersecurity for the Medical Device Industry
The attack on Boston Scientific serves as a wake-up call for the entire medical device industry. Here are several key lessons that can be drawn from this incident:
- Proactive Cybersecurity Measures: Companies must invest in robust cybersecurity frameworks that include regular assessments and updates to security protocols.
- Incident Response Planning: Organizations should have comprehensive incident response plans in place, ensuring that they can quickly address and mitigate any breaches.
- Transparency and Communication: Clear communication with stakeholders, including patients and healthcare providers, is essential during a crisis.
- Employee Training: Regular training for employees on cybersecurity best practices can help prevent breaches from occurring.
- Collaboration with Cybersecurity Experts: Partnering with cybersecurity firms can provide additional resources and expertise to fortify defenses.
Key Takeaways
- Boston Scientific is experiencing a significant cyberattack causing global operational disruptions.
- The nature and extent of the attack remain unclear, raising concerns about patient safety.
- This incident reflects a broader trend of rising cybersecurity threats in the healthcare sector.
- Proactive cybersecurity measures are essential for protecting sensitive patient data and ensuring the reliability of medical devices.
Frequently Asked Questions
What immediate steps should Boston Scientific take in response to the cyberattack?
In response to the cyberattack, Boston Scientific should prioritize restoring access to its IT systems while conducting a thorough investigation to determine the attack's origin and impact. Engaging cybersecurity experts to assist in the investigation and remediation process is crucial. Additionally, the company must communicate transparently with stakeholders, including patients and healthcare providers, about the status of the investigation and any potential risks.
How can patients protect themselves in light of this incident?
Patients who have Boston Scientific devices should stay informed about the situation by checking the company's website and following any communications from their healthcare providers. It's essential for patients to consult with their doctors regarding any concerns they may have about their medical devices, especially if they experience any issues or anomalies. Additionally, patients should be cautious about sharing sensitive information online and remain vigilant against potential phishing attempts that may arise from the incident.
What are the implications for the healthcare industry as a whole?
The rising trend of cyberattacks on healthcare organizations underscores the urgent need for enhanced cybersecurity measures across the industry. As healthcare becomes increasingly reliant on technology, the potential risks associated with cyber threats must be addressed proactively. This includes investing in secure systems, training employees on cybersecurity practices, and developing incident response plans to protect patient safety and data integrity.
Comments
Meta's $18 Billion Settlement: New Protections for Minors on Social Media
Meta has agreed to implement significant changes to enhance child safety on its platforms as part of an $18 billion settlement. These changes, including time limits and content controls, will impact millions of young users across the U.S.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation