Turning FTP Vulnerabilities into Attack Vectors: The Rise of E4del and PINHOLE RATs
As cyber threats evolve, the emergence of E4del and PINHOLE RATs showcases a concerning trend in malware distribution. This article explores how these threats exploit FTP banners and what businesses can do to safeguard their systems.
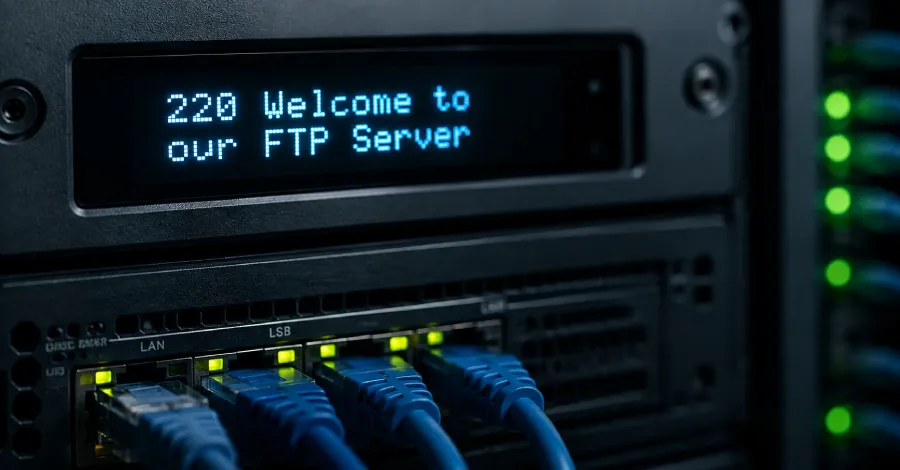
In the ever-evolving landscape of cybersecurity, one of the most alarming trends is the adaptation of malware to exploit seemingly innocuous system components. Recent revelations about E4del and PINHOLE Remote Access Trojans (RATs) highlight how these threats leverage File Transfer Protocol (FTP) banners as conduits for distributing malicious commands. This article delves into the mechanics of these threats, their implications for businesses, and best practices for mitigating risk.
Understanding FTP: A Gateway for Attackers
File Transfer Protocol (FTP) is a standard network protocol used to transfer files between a client and server. While FTP plays a crucial role in web development and data management, its inherent vulnerabilities can be exploited by cybercriminals. By embedding malicious commands within FTP banners, attackers can create a pathway for Remote Access Trojans (RATs) like E4del and PINHOLE to infiltrate systems.
FTP banners, which are typically used to provide information about the server, can be manipulated to include executable code. When unsuspecting users connect to an FTP server, they may inadvertently trigger these commands, granting attackers remote access to their systems. This method of attack is particularly insidious because it exploits the trust users place in legitimate FTP services.
The Mechanics of E4del and PINHOLE RATs
E4del and PINHOLE are not the first RATs to exploit FTP vulnerabilities, but their methods stand out due to their sophistication and stealth. E4del, for instance, uses a multi-stage infection process that begins with the delivery of a payload via FTP banners. Once the initial connection is made, E4del can download additional modules to establish a foothold within the target system.
PINHOLE’s Unique Approach
PINHOLE, on the other hand, utilizes a more aggressive approach by leveraging stolen credentials to access FTP servers directly. Once inside, it can manipulate the server settings to embed its commands within the FTP banner. This dual-layer attack not only compromises the server but also targets clients who connect to it, creating a widespread impact.
The Impact of Identity Exposure on Cybersecurity
The rise of E4del and PINHOLE RATs underscores a broader issue: identity exposure. When personal or organizational identities are compromised, it can unlock active attack paths that are difficult to trace. Attackers often exploit these paths to escalate privileges across different domains, effectively breaching security measures that would otherwise protect sensitive data.
Recent studies have shown that organizations can suffer significant financial losses due to identity exposure. For instance, a survey revealed that businesses could face damages ranging from $3 million to over $5 million in the event of a major data breach. This alarming statistic highlights the necessity for organizations to prioritize identity protection and implement robust security protocols.
Strategies for Mitigating Risks
Given the rising threat of E4del and PINHOLE RATs, organizations must take proactive measures to safeguard their systems. Here are some effective strategies:
- Regular System Audits: Conduct frequent audits of your FTP servers to identify vulnerabilities and ensure that only authorized users have access.
- Implement Multi-Factor Authentication (MFA): Utilize MFA to add an additional layer of security, making it more difficult for attackers to gain unauthorized access.
- Educate Employees: Provide training to staff about the risks of FTP vulnerabilities and how to identify suspicious activity.
- Use Secure Protocols: Whenever possible, transition to more secure file transfer protocols such as SFTP or FTPS, which encrypt data during transmission.
Key Takeaways
- FTP vulnerabilities are being exploited by advanced RATs like E4del and PINHOLE.
- Identity exposure can unlock critical attack paths, making it essential to protect sensitive information.
- Organizations must implement robust security measures to mitigate the risks posed by these evolving threats.
- Education and training are vital in equipping employees to recognize and respond to cyber threats.
Frequently Asked Questions
What are E4del and PINHOLE RATs?
E4del and PINHOLE are Remote Access Trojans that exploit vulnerabilities in FTP banners to deliver malicious commands. They represent a growing trend of sophisticated malware that targets organizations through seemingly innocuous means.
How can organizations protect themselves against these threats?
Organizations can protect themselves by conducting regular system audits, implementing multi-factor authentication, educating employees about potential threats, and using secure file transfer protocols to encrypt data during transmission.
What role does identity exposure play in cyberattacks?
Identity exposure can serve as a gateway for attackers, allowing them to escalate privileges and access sensitive data across different domains. Protecting against identity theft is critical to maintaining a secure environment.
Are FTP servers inherently insecure?
While FTP servers are widely used, they can be inherently insecure if not properly configured and monitored. Organizations should take care to limit access, regularly update their security protocols, and consider transitioning to more secure alternatives like SFTP or FTPS.
Comments
Critical Security Flaw in Oracle WebLogic: Immediate Risks and Mitigation Strategies
An actively exploited vulnerability in Oracle WebLogic is exposing critical data to unauthenticated attackers. This article delves into the implications of this flaw and offers strategies for safeguarding your systems.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation