AI-Generated Exploit Scripts Target Siemens S7 PLCs in U.S. Critical Infrastructure
Recent developments in cybersecurity have unveiled a troubling trend: the emergence of AI-generated exploit scripts aimed at Siemens S7 Programmable Logic Controllers (PLCs) within critical infrastructure systems. This article delves into the implications of these threats and outlines essential strategies for organizations to safeguard their operational technology.
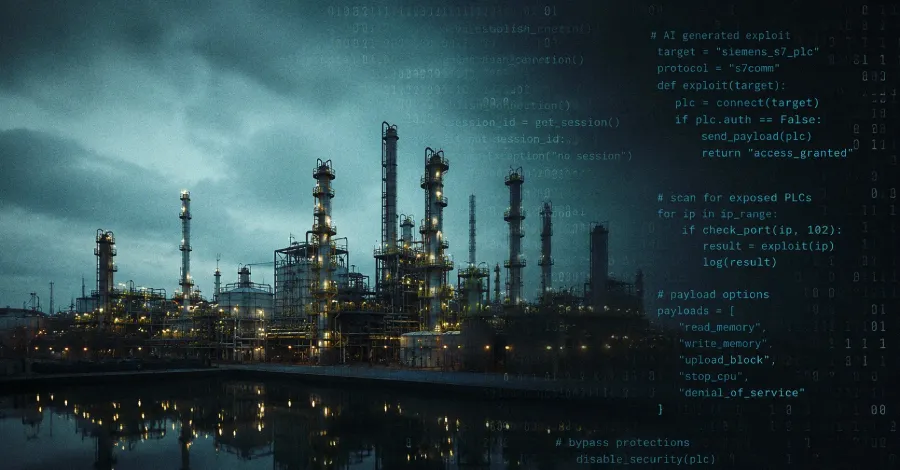
The rise of artificial intelligence (AI) in cybersecurity has taken on a double-edged sword dynamic, with attackers now leveraging the technology to generate sophisticated exploit scripts. Recently, cybersecurity experts identified AI-generated scripts specifically targeting Siemens S7 Programmable Logic Controllers (PLCs), which are pivotal in the management of critical infrastructure across the United States. This alarming trend not only raises red flags for organizations relying on these systems but also underscores the urgent need for enhanced security measures to protect against evolving threats.
Siemens S7 PLCs are integral to a variety of industrial processes, including power generation, water treatment, and manufacturing. As these systems become increasingly interconnected, they present attractive targets for cybercriminals seeking to exploit vulnerabilities. The advent of AI-generated exploits complicates the landscape—these tools can quickly adapt to existing security measures, leading to a heightened risk for critical infrastructure and the communities that depend on them.
The Role of AI in Cyber Threats
The integration of AI into cyberattacks represents a significant shift in the tactics employed by cybercriminals. Traditional exploit development required a deep understanding of programming and system vulnerabilities, often limiting the pool of potential attackers. However, AI can automate and accelerate the creation of exploit scripts, making sophisticated attacks more accessible to less skilled individuals.
How AI-Generated Exploits Work
AI-generated exploits are fueled by machine learning algorithms that analyze vast amounts of data to identify vulnerabilities in software and hardware systems. These algorithms can:
- Analyze Patterns: By studying existing vulnerabilities in PLCs, AI can predict potential weaknesses in similar systems.
- Automate Script Generation: Instead of manual coding, AI creates tailored scripts that can bypass security measures with alarming efficiency.
- Adapt Over Time: As defenses evolve, AI can modify its scripts to maintain effectiveness, creating a cat-and-mouse dynamic.
Impact on Critical Infrastructure
The implications of AI-generated exploit scripts targeting Siemens S7 PLCs are profound. These PLCs control essential functions in sectors critical to national security and public safety, such as:
- Energy Sector: Overseeing power plants and electrical grids, any compromise could lead to widespread outages.
- Water Treatment Facilities: Contaminating water supplies or disrupting service could have catastrophic public health implications.
- Manufacturing Plants: Disabling production lines can result in significant economic losses and supply chain disruptions.
With the potential for widespread damage, organizations must prioritize cybersecurity efforts surrounding their PLC systems. The interconnectivity of modern infrastructure means that a breach in one area can lead to cascading failures across multiple sectors.
Real Stories of Identity Exposure
Compounding the risk from AI-generated scripts is the issue of identity exposure. Organizations often overlook how improper identity management can create active attack paths that cybercriminals can exploit. For instance, a single compromised account can serve as a gateway for privilege escalation, enabling attackers to move laterally within a network.
Mapping Attack Paths
To mitigate risks, cybersecurity professionals are developing strategies to map cross-domain privilege escalation routes. Understanding these pathways can help organizations sever potential breach routes at key choke points. Here are some critical steps to consider:
- Regular Audits: Conducting frequent audits of user permissions can help identify and rectify excessive access rights.
- Implementing Least Privilege: Ensuring that users only have access to the systems necessary for their roles can minimize attack vectors.
- Multi-Factor Authentication: Enforcing multi-factor authentication (MFA) can add an additional layer of security, making it more challenging for attackers to exploit compromised identities.
Protecting Against Emerging Threats
Organizations must adopt a proactive approach to cybersecurity, especially concerning AI-generated threats. Here are actionable strategies to enhance protection against these evolving risks:
- Invest in Advanced Threat Detection: Utilizing AI-driven security tools can help detect unusual behavior and potential exploits before they cause damage.
- Employee Training: Regular training sessions can educate staff about the latest threats and best practices for maintaining security.
- Incident Response Plans: Developing and regularly updating incident response plans can ensure swift action if a breach occurs.
By implementing these strategies, organizations can build a robust defense against not only AI-generated exploit scripts but also the broader spectrum of cyber threats targeting critical infrastructure.
Key Takeaways
- AI-generated exploit scripts pose a new threat to Siemens S7 PLCs in critical infrastructure.
- Understanding and mapping identity exposure can help organizations mitigate attack paths.
- Proactive cybersecurity measures are essential to safeguarding against evolving threats.
- Interconnectivity in infrastructure means breaches can lead to widespread consequences.
Frequently Asked Questions
What are Siemens S7 PLCs, and why are they targeted?
Siemens S7 PLCs are programmable logic controllers used in various industrial applications, including power generation and manufacturing. Their critical role in managing essential infrastructure makes them attractive targets for cybercriminals, especially as the systems become more interconnected and vulnerable to attacks.
How can AI improve cybersecurity defenses?
AI can enhance cybersecurity by automating threat detection, analyzing large datasets for patterns of behavior, and adapting to new vulnerabilities more quickly than traditional methods. This can lead to more effective and timely responses to potential threats.
What steps should organizations take to protect their PLC systems?
Organizations should prioritize regular audits of user access, implement the principle of least privilege, enforce multi-factor authentication, and invest in advanced threat detection tools. Additionally, employee training and incident response planning are crucial for maintaining security.
What are the consequences of a breach in critical infrastructure?
A breach in critical infrastructure can lead to severe consequences, including power outages, contamination of essential services like water supply, and significant economic losses due to production halts. It can also pose risks to public health and safety, underscoring the importance of robust cybersecurity measures.
Comments
The Rise of Meta AI Glasses: Privacy Concerns and Detection Solutions
As Meta AI glasses gain popularity, concerns about privacy and unauthorized recordings are escalating. This article explores the implications of these devices and emerging solutions to protect individuals.
Related articles
Popular in Cybersecurity
- Federal Mandate for Autonomous Vehicles: A Call for Safety Compliance
- EU Mandates Google to Share Data and Open AI on Android: What It Means
- GitHub Revamps Bug Bounty Program: Implications for Developers and Security
- Australian Government Disables Thousands of Functional Broadband Routers: A Wasteful Decision
- Exploiting Redis: Understanding Zero-Day Vulnerabilities and Their Mitigation